
1. Traditional FreeBSD Maintenance
Traditional FreeBSD deployments face two approaches:
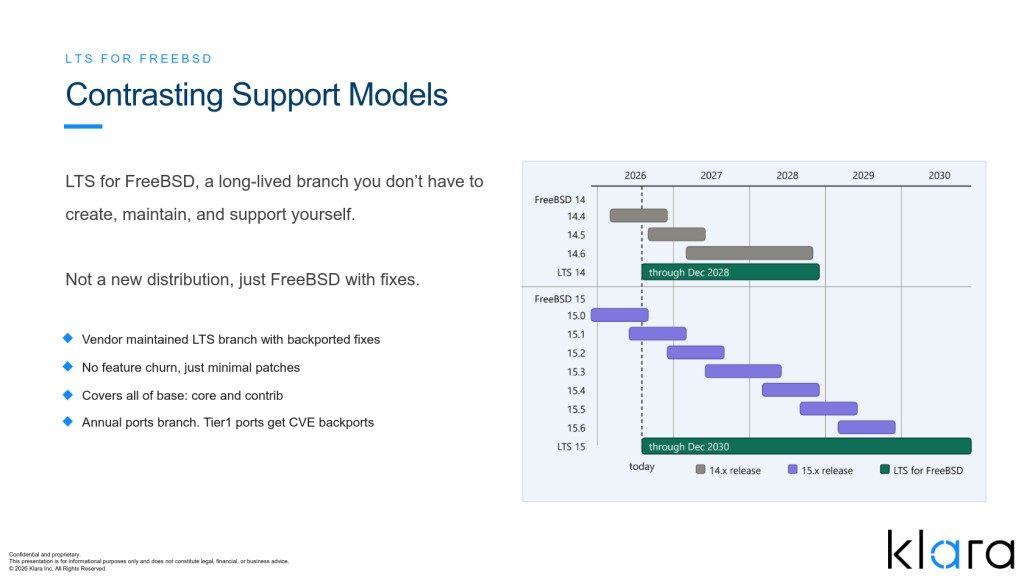
- Regular upgrades: Every 6–9 months, qualify, regression-test, and deploy new releases.
- Freeze existing systems: Avoid regressions but sacrifice security fixes, bug fixes, and support.
- Self-maintenance: Organizations must handle release engineering, security, QA, and ports maintenance themselves.
2. Klara’s LTS for FreeBSD
Klara introduces a vendor-maintained, long-term support branch for FreeBSD.
- Remains standard FreeBSD, not a separate distribution.
- Backports security patches and critical bug fixes.
- Avoids unnecessary features and disruptive upgrades.
- Covers the complete base system, including contributed components.
- Offers an annual ports branch with CVE backports for Tier 1 ports.
3. Key Features
| Feature | Description |
|---|---|
| 5-year LTS | FreeBSD 14 supported through 2028+; FreeBSD 15 through 2030+, with optional extensions |
| No minor upgrades | Security and maintenance patches replace frequent release upgrades |
| Pkgbase updates | Binary package-based updates, including air-gapped environments |
| Security backports | CVE fixes, critical bugs, errata, and ZFS issues |
| Quarterly rollups | Bundled less-critical fixes |
| CVE impact analysis | Assessment and rescoring based on infrastructure exposure |
| Custom patches | Organization-specific patches with binary updates |
| Enterprise support | Documentation, email support, and optional SLAs |
| Artifact provenance | Traceability of distributed binary artifacts |
4. Upgrade Paths
- FreeBSD 14.x → 14LTS: Minimal changes.
- FreeBSD 13.x, 14.x, or 15.x → LTS15: Supported as a single upgrade.
- Air-gapped systems: Offline updates supported through pkgbase.
5. What Klara LTS Is Not
- Not a FreeBSD fork: No separate Klara BSD distribution.
- Not private security development: Klara does not intend to withhold fixes from the community.
- Not a criticism of FreeBSD: It addresses long-term maintenance beyond the project’s available resources.
- Not complete LTS for all ports: Ports receive annual branches and prioritized CVE backports rather than universal long-term maintenance.