
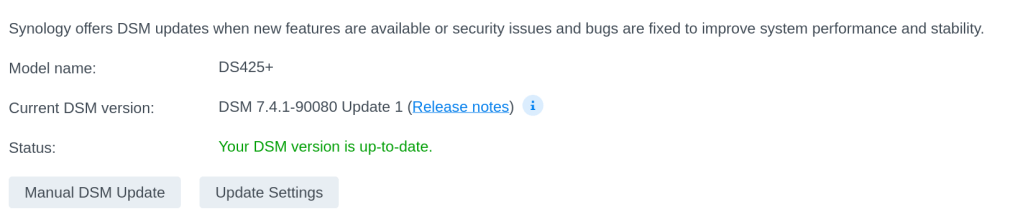
“Synology has identified threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM. These attacks aim to encrypt data and extort ransom.”
https://www.synology.com/en-global/company/news/article/C3RB3R

