Release Info
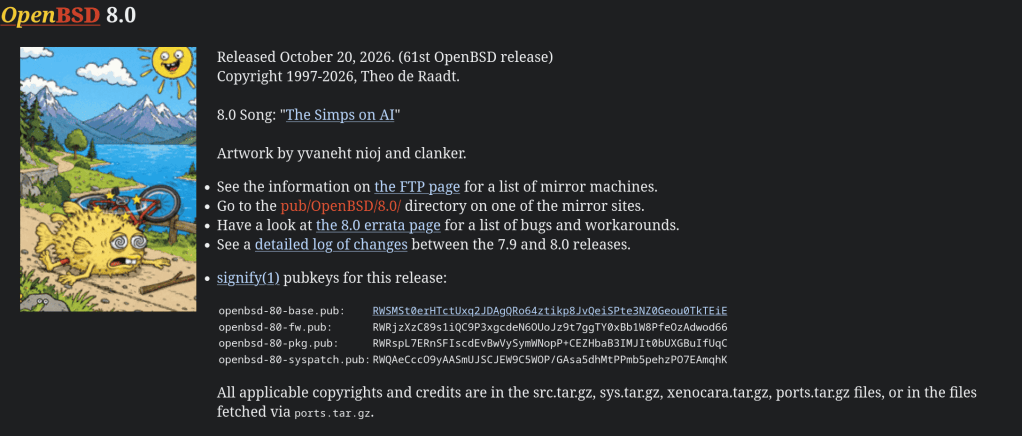
- Released October 20, 2026; 61st OpenBSD release
- Release song: “The Simps on AI”
- Separate signify(1) public keys for base, firmware, packages, and syspatch
- Errata page and a full 7.9 → 8.0 changelog are available
Platform-Specific
- amd64: Kernel virtual address space raised from 4G to 512G; pmap direct map randomized; AES-accelerated swap encryption
- arm64: Hibernate support; AES-accelerated swap encryption; bounce buffers
- luna88k: m88k CMMU fixes (register writes, write-protection faults, CPU #0 init, faster CPU lookup)
- riscv64: CPU extension detection via elf_aux_info(3); ‘V’ vector extension; bounce buffers; Advanced Interrupt Architecture (new imsic(4), aplic(4)); Sstc timer extension
- sparc64: Switched to LLVM toolchain; relocation bounds check; better SPARCV9 memory alignment
- Other: loongson retired (incompatible with Clang 22); RISC-V/MIPS LLVM fixes; hppa protection-bit encoding fix
Kernel
- Fixes to open_wmemstream(3) sizing and semop(2) semaphore IDs during context switch
- Better pagedaemon inactive-queue heuristics
- New getexecpath(3)
- Further groundwork for larger disklabels
Suspend/Hibernate
- Suspend/resume for qwz(4) and qcuart(4); ufshci(4) survives suspend on specific Snapdragon laptops
- bytgpio(4) wakeup interrupts (fixes IdeaPad resume)
- Lid close no longer wakes the machine when machdep.lidaction=0
- Global sleep-mode variable distinguishes hibernate from suspend
- Unhibernate hardening: size validation, overflow and overread protection, framebuffer cleanup
- nvme(4) hibernate queue allocation failure is no longer fatal
Graphics (DRM)
- drm(4) updated to Linux 6.18.53
- Intel Arc A-Series (DG2/Alchemist) support in inteldrm(4)
- More than 4GB of VRAM can be mapped on amd64
- Workaround for GuC timeouts on some Alder Lake systems
VMM/VMD
- Up to 64 vCPUs per guest; x2apic mode
- VM ownership redesigned around files
- MSI/MSI-X virtio interrupts, checksum offload, split virtqueues, better qcow handling
- ioapic/lapic emulation added; fixes for 32-bit Linux guests
- Exit handling refactored; variable-length VMX instructions supported
- ELF loaders hardened against malformed files
Userland
- netstat(1) shows interface multicast counters
- mount(8) accepts DUIDs with -u
- sndioctl(1)/sndiod(8): midithru control, editable lists, dynamic server.mode
- ddb(4)
ps output split by process/proc
- Fixes in patch(1) (infinite loop), getpwent(3) (memory leak), ld.so loading checks, npppd(8), pstat(8), eigrpd(8), sndiod(8)
- Several daemons now use absolute-path execv(3)
Hardware and Drivers
- New drivers: samsabi(4), sambat(4) (Samsung), rkotp(4) (Rockchip)
- SoC/board support: SpacemiT K1/K3, Qualcomm SC7280 and Glymur (X2), RK3528/Radxa E24C, RK8600 regulator, AMD Krackan Point
- Apple: apldart(4) page-table mirroring; IOMMU for USB
- Fixes: Samsung and HONOR touchscreen/touchpad, esp(4) FIFO overflow, softraid(4) rebuild (memory leak, 4K sectors), re(4) 64-bit DMA
- Ethernet: em(4) adds Panther Lake and Wildcat Lake; ix(4) adds Intel E610
- Wireless:
- qwx(4) gains 802.11n, 40MHz channels, and roaming fixes, plus many stability fixes (DMA, races, locking, firmware crashes)
- qwz(4) gains 802.11n/40MHz and native-WiFi QoS
Installer and Package Tools
- Consistent installurl(5) handling across pkg_add(1), sysupgrade(8), and syspatch(8)
- fw_update(8) hardened: size limits, stricter signature checks, path restrictions, better errors
- pkg_add(1) handles merge-set loops; current directory removed from default search path
- syspatch(8) no longer downloads the full tgz just to check for updates
Security
- pledge(2): Fixes and extensions (vfs, lldpd ‘mcast’, sockopt checks, Ethernet multicast)
- Crypto: ipsec(4) AES GMAC; libcrypto fixes for RSA-PSS, delta CRLs, RFC 3779, x509 memory leak
- Exec/ELF hardening:
- ld.so $ORIGIN via execve(2)
- Script pathname TOCTOU fixed; more robust execve(2) realpath handling
- Stricter ELF notes and interpreter checks
- kbind(2)/pinsyscalls(2) disabled for static binaries
- Kernel stack leak in elf(5) structs fixed
- m88k: Unprivileged kernel memory read/write vulnerability removed from the 88100 data pipeline; luna88k kernel built with -fno-pie
- unveil(2): Now restricts man(1), makewhatis(8), man.cgi(8)
- Daemons: iked(8) rejects malformed and out-of-state IKEv2 messages; dhcpd(8) crash and memory exhaustion fixes; dhcpleased(8) validates the acked IP
- Archives and patches: pax(1) over-read and path-traversal extraction fixed; syspatch(8) script hardening
- CVE fixes: libexpat 2.8.4 (3 CVEs), perl(1) (Storable, pack/unpack, regex, Socket 2.041), libXfont2, Xserver, nsd(8)
- isakmpd(8): Transport leak plugged; ID payload size enforced; multiple bounds checks
- Privilege separation:
- syslogd(8) parent gets its own executable
- smtpd(8) IPC hardened (cleared userinfo, sockaddr size checks, zeroed buffers, lookup teardown) and environment characters restricted
- Other: sysctl(2) KERN_PROC_ARGS overflow, aplmca(4) bounds, memmem(3)/strstr(3) shift overflows, profil(2) leaks and race, ktrace(1) stack info leak
Network Stack
- New:
- ice(4): full duplex, TSO tuning (128 DMA segments)
- bge(4) BCM5720: 64-bit DMA
- ogx(4): jumbo frames
- Fixes:
- bpf(4): bounds checks (libpcap CVE), filter validation, later tap point for outgoing packets
- ipsec(4): packet size overflow
- Drivers: tun(4) leak, ixl(4) MTU, iwx(4) channel width, em(4) K1 timeout
- veb(4): kernel stack leaks and packet corruption
- ospfd(8)/ospf6d(8): imsg handling, rtlabel updates, address-layout leak
pf(4)
- Fixes for ioctl off-by-one, unterminated strings, NULL deref, and out-of-bounds read
- Valid MLD packets and TCP state no longer dropped (crafted-reset fix)
- Connection counter races fixed
- Fragment reassembly now happens in the correct rdomain
pfctl -s all no longer dumps all OS fingerprints
Userland Network Daemons
- httpd(8):
- New: custom headers
- RFC 9112 compliance: rejects CL.TE framing and obs-fold
- Chunked upload and suffix range fixes
- Vary/Last-Modified handling
- Default TLS ciphers now
secure
- relayd(8):
- New: Lua patterns in filter rules, ECDSA CA engine, MKCALENDAR method, multiple resolvable addresses
- RFC 9112 hardening; default TLS ciphers now
secure; new imsg API
- smtpd(8):
- Input validation (usernames, CR/LF, DNS, queue buffers) and leak fixes
- Code adjusted to avoid false reports from LLM scanners
- Shared:
- httpd(8) and smtpd(8) are random-relinked at boot
- Major daemons now use getexecpath(3)/execv(3)
- IMSG_CTL_PROCFD restricted to the parent process
- New daemon: rtrd(8)/rtrctl(8), an RPKI-To-Router daemon
- acme-client(1): External account binding, wildcard alt names, HTTP request injection fix
- bgpd(8): Extensive fixes, including:
- Use-after-free, overflows, ASPATH limited to 750 elements
- Graceful restart and add-path rework
- RTR v2 error codes
- Peer data leak to bgpctl(8)
- rpki-client(8): Stricter certificate/ROA validation, OpenSSL 4.1 overread fix, backoff retries for failing CAs, more jitter, assorted bug fixes
- Other: agentx(3)/snmpd(8) underflow, dhcpleased(8) route handling, login_radius(8) length checks, PFKEY infinite-loop fix across iked/isakmpd/bgpd/ldpd
tmux(1)
- New: modal and floating panes (
new-pane, -O, -K), borderless menus, refresh-now, capture-pane options (-H, -L, -F), kill-session -g, Emacs-style re-centre
- Reworked: prompts
- Fixed: multiple crashes, an infinite loop, leaks
LibreSSL 4.4.0
- Security:
- X.509 name-constraint URI bypass
- DTLS memory exhaustion
- OCSP stapling authorization bypass (affects nc(1)/ftp(1) with
muststaple)
- Compatibility:
- libtls prefers X25519MLKEM768 for TLSv1.3
- tls_peer_cert_chain_pem() deprecated
- Prepared for future OpenSSL ASN.1 behavior
- Portable: openssl(1), nc(1), ocspcheck(8) no longer run silently without pledge/unveil
- Internal: Many DTLS/TLS/PKCS#7/CRL fixes; faster SHA-3
OpenSSH 10.6
- Security:
- LZ77 compressor disabled (side-channel risk)
- ChannelTimeout and RekeyLimit now applied
restrict now covers tunnel forwarding
- Incompatible:
- IANA codepoint for ssh-mldsa44-ed25519
- DisableForwarding overrides PermitTunnel
- Agent username size limit; NUL rejected in
scp -O
- New:
- Experimental post-quantum mldsa44-ed25519 signatures
ssh -Z lists keys to be triedssh-add -P skips PIN entry- ed25519 now via libsodium
- ssh-keygen
hexdump
- Bugfixes: Use-after-free and NULL deref fixes, sshd config refactor, reduced pre-auth attack surface
Packages
- Counts: amd64 13,060; aarch64 12,907; riscv64 11,116; i386 10,659; sparc64 10,621; powerpc64 9,564; mips64 9,072
- arm and powerpc counts are still the placeholder “XXX”
- Highlights: GNOME 49, KDE Plasma 6.7.5, Firefox 157.0, Chromium 154, LLVM 21/22, GCC 16.1, Go 1.27.1, Rust 1.98.1, Python 3.14.7, PostgreSQL 18.6, Emacs 31.1, TeX Live 2026, Wayland 1.26.0 with six compositors
Base Components
- Xenocara (xserver 21.1.24, Mesa 25.0.7)
- LLVM/Clang 22.1.6
- Perl 5.42.3
- NSD 4.15.2, Unbound 1.26.1
- Expat 2.8.4, zlib 1.3.2
Install, Upgrade, Source
- Per-architecture install media: ISO, USB image, miniroot, floppy, or network boot; details in each INSTALL.<arch> file
- Upgrades from 7.9 are covered in the Upgrade Guide
- src, sys, and ports tarballs are CVS checkouts; track -stable with
-rOPENBSD_8_0
https://www.openbsd.org/80.html